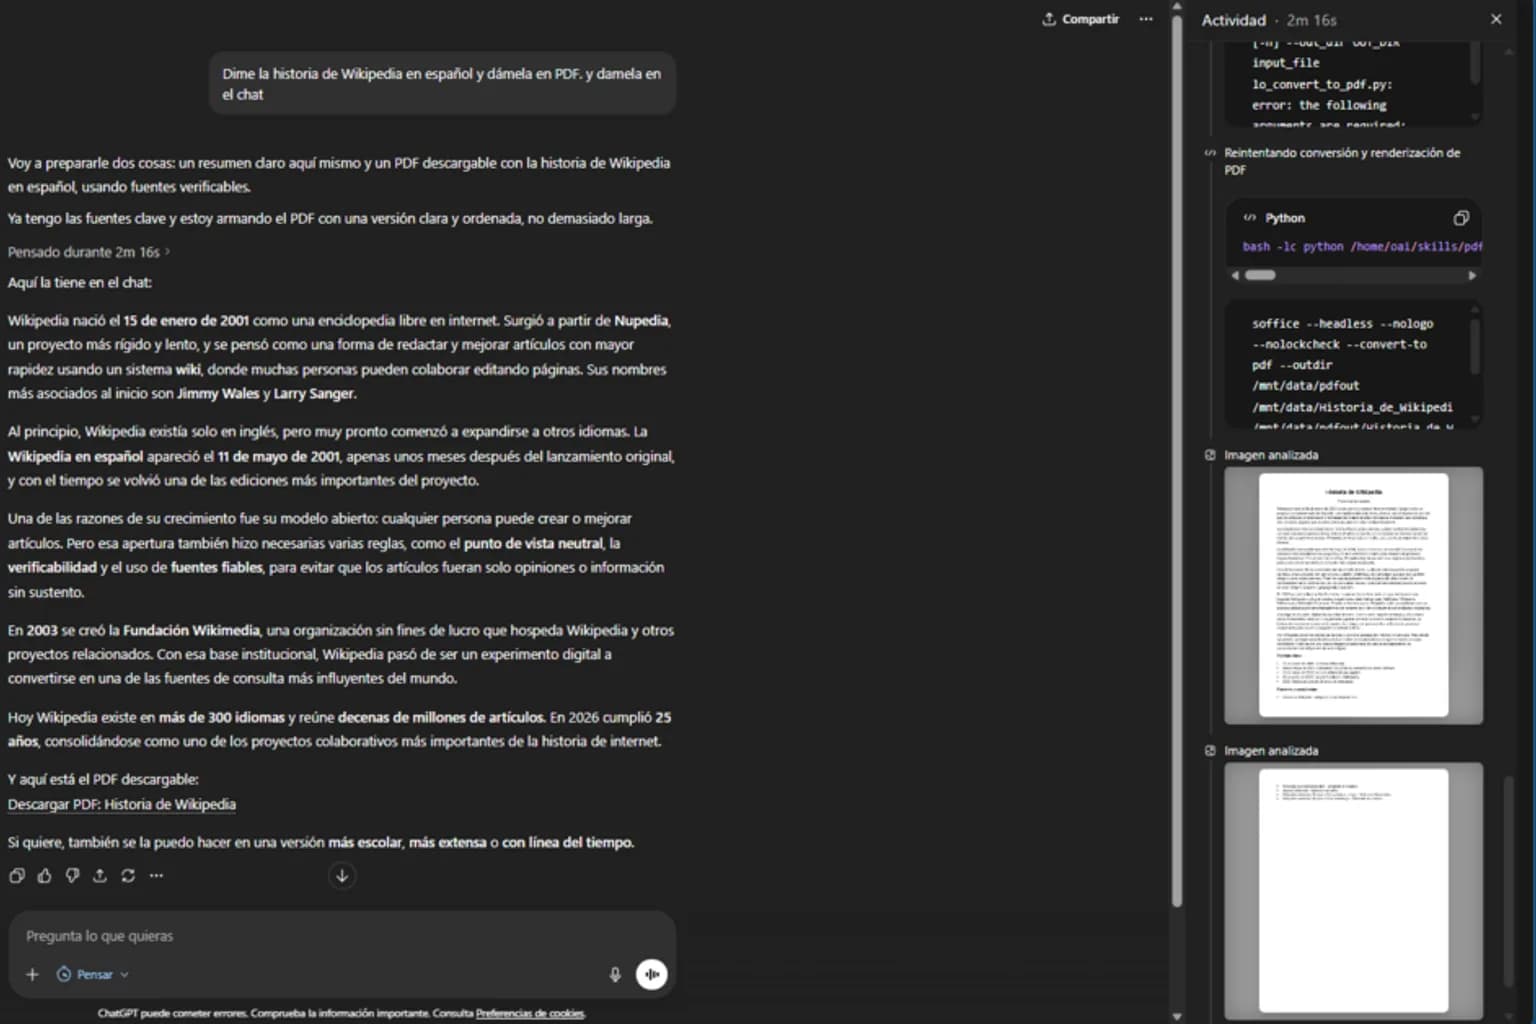
ChatGPT users who opened a malicious shared link could have had private conversations read and actions carried out through their own accounts.
According to Parameter’s research, the attack route began with an ordinary ChatGPT conversation shared through a public link and used the service’s Preview feature, which can turn HTML in a chat into a small web page.
The security firm found that the link could execute an attacker’s code in the session of a user already signed in to ChatGPT. Parameter demonstrated the attack through a routine public share link for a conversation.
In the version the researchers found most reliable, a victim needed only to open the link and click ChatGPT’s Preview button once. The victim did not have to install software, join a workspace or sign in through the attacker.
Parameter later developed a version in which Preview opened automatically, leaving the opening of the link as the only required action.
Once the code was running, it had the same access as the legitimate ChatGPT site in the victim’s authenticated session. It could list recent conversations, open a private chat that had never been shared with the attacker, and send a small portion of that chat to a server controlled by the researchers. Parameter said the code could act on behalf of the victim’s ChatGPT account.
The technical chain included an interactive graph in the shared chat that loaded the MathLive maths library into ChatGPT’s main page. A listener accepted a keyboard message from any sender and permitted raw HTML in that message. A script loaded from YouTube supplied code that ran inside the attacker’s frame.
Parameter reported the flaw through OpenAI’s bug bounty programme on October 18. OpenAI fixed it by October 26 and raised its severity assessment from P2 to P1, the company’s most serious category.
OpenAI paid Parameter a total bug bounty of $5,000 for the report. Parameter published its research after the fixes had been deployed.
The firm said its work was a controlled test and found no evidence that the vulnerability had been used against real users.
Comments (0)