
For job seekers and the companies that hire them, a coding test sent during a recruitment process can give attackers access to a victim's computer.
US intelligence officials in the Biden and second Trump administrations have said North Korea's remote IT worker scams are a primary way of funding Pyongyang's weapons programme, alongside cryptocurrency theft.
The scale of the hiring push has risen sharply across Pindrop Security's customer base. North Korean applicants accounted for 1 in every 343 applications last year and 1 in 47 this year.
Recorded Future's Insikt Group found that one cluster of North Korean IT workers applied to jobs at more than 1,100 companies between late 2024 and early 2025. The operators maintained at least 22 fabricated personas, with some applying to at least 60 positions a day and highly likely to be working for at least 10 organisations at once.
Those identities were supported by AI-generated profile photographs, custom-configured ChatGPT assistants and documents obtained from an illicit identity-generation service. Recorded Future also found that operators used real-time AI transcription to supply answers during interviews. Advances in AI-powered video and audio tools have helped North Koreans expand a separate fraud in which US companies are tricked into hiring them for IT roles.
TraderTraitor actors, linked in the brief to the Lazarus Group, have posed as recruiters offering well-paid roles in order to persuade targets to download malicious software. They have approached developers and employees at cryptocurrency firms through professional networking sites including LinkedIn, presenting what appeared to be genuine opportunities.
The bait is a technical interview. A candidate receives a coding test to run on their own machine, while the files contain malware designed to give attackers access to the computer.
That approach featured in a 2024 theft of US$308 million from the Japanese cryptocurrency exchange DMM Bitcoin. A North Korean hacker posing as a recruiter contacted an employee at a separate virtual currency wallet software company through LinkedIn and sent a supposed pre-employment test carrying malicious code.
Engineer B, a Binance software engineer, encountered a similar process after being approached through a job platform in September. In the first video interview, the apparent recruiter showed a social-media account containing photographs from their personal life, an effort to build trust.
During a second video interview, someone claiming to be a chief executive told Engineer B to download software for a test assignment. The software contained malicious code. The code exploited a zero-day vulnerability that security tools did not detect.
The campaign, known as Contagious Interview, was reportedly active from December 2025 to July 2026. It reportedly infected over 30,000 devices, affected 7,000 crypto wallets and moved around $10.7 million.
Some recruitment checks have exposed the deception in stranger ways. At one software company, a candidate completed every technical interview round before leaving a video call when asked to insult the North Korean leader.
The operation also reaches beyond applicants targeted by fake recruiters. At a large New Zealand business, a remote IT contractor using a false identity and false documents worked through a recruited New Zealand citizen who received and operated the company laptop. An Australian healthcare company found that three staff members were North Koreans impersonating Chinese nationals.
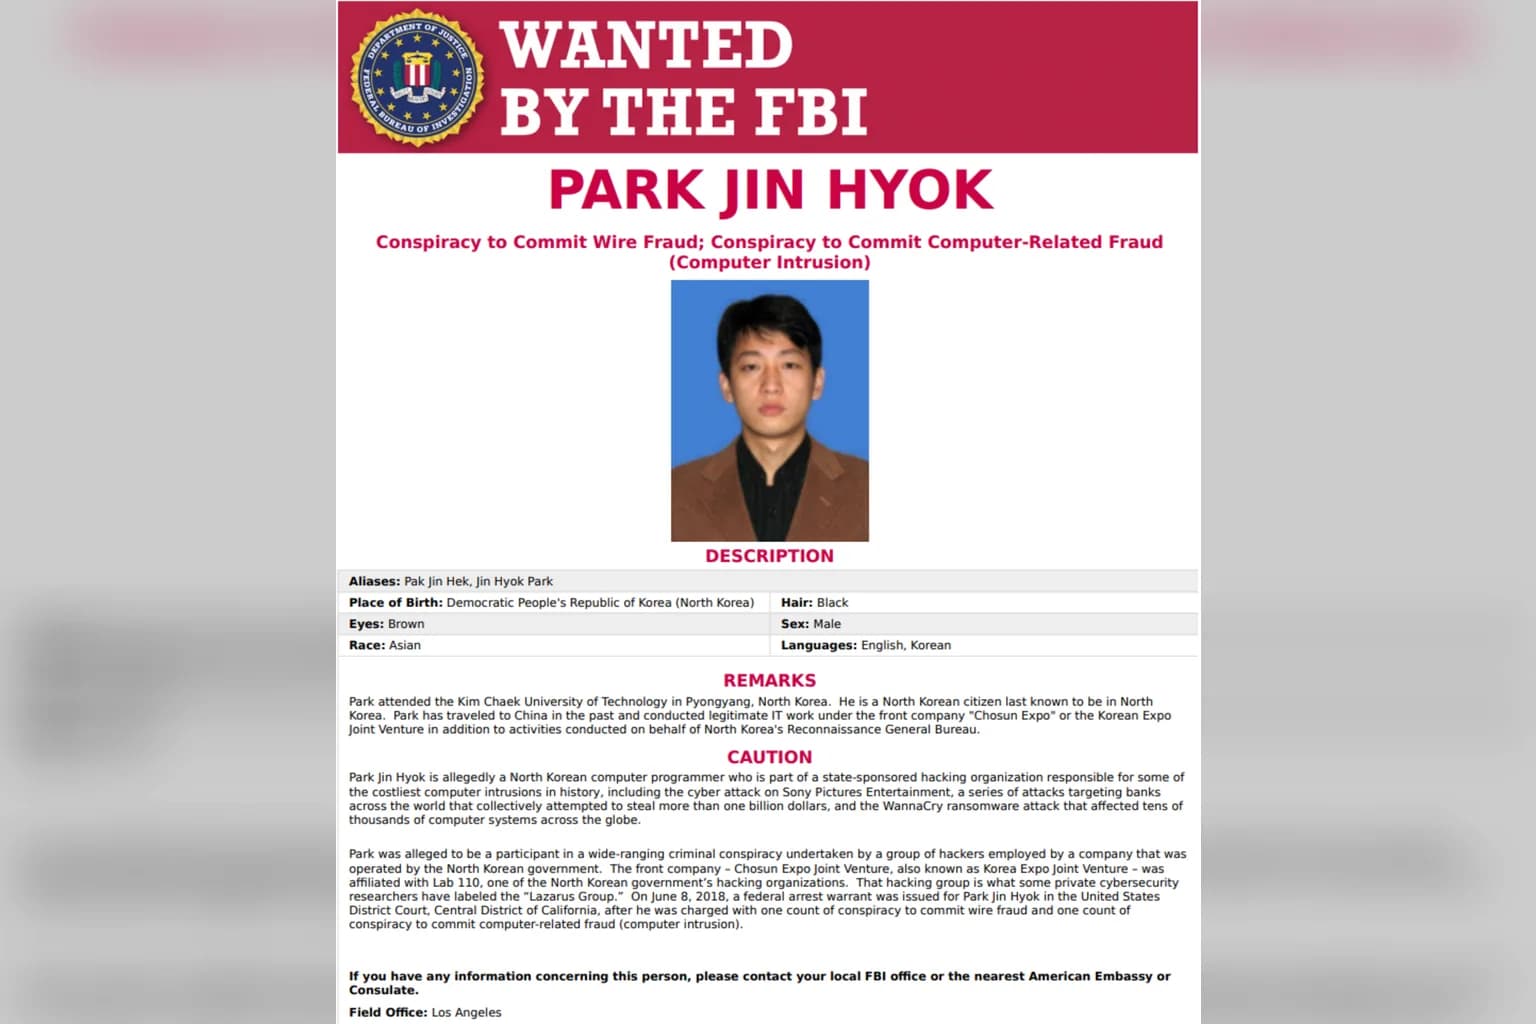
The FBI last month disrupted a network of American facilitators accused of helping the North Korean government obtain remote IT work, dismantling more than 40 so-called laptop farms across Texas. The Justice Department unsealed charges against two US nationals and 10 China-based North Koreans accused of identity theft to collect pay from unwitting US employers. Prosecutors said 70 companies were bilked out of more than $3 million from 2019 to 2025.
North Korea has generated billions in cash in recent years through remote IT worker schemes. US authorities estimate the scheme generated US$800m in 2024. US and international intelligence officials determined that the scams had become a primary funding method for Pyongyang's weapons programme, with estimates of US$800 million to US$864 million generated in 2024.
Comments (0)