
For Binance customers, a fake recruitment campaign and a tampered software installer culminated in the theft of $6.3 billion in virtual assets from the world’s largest cryptocurrency exchange, in what has been described as the largest hack in history.
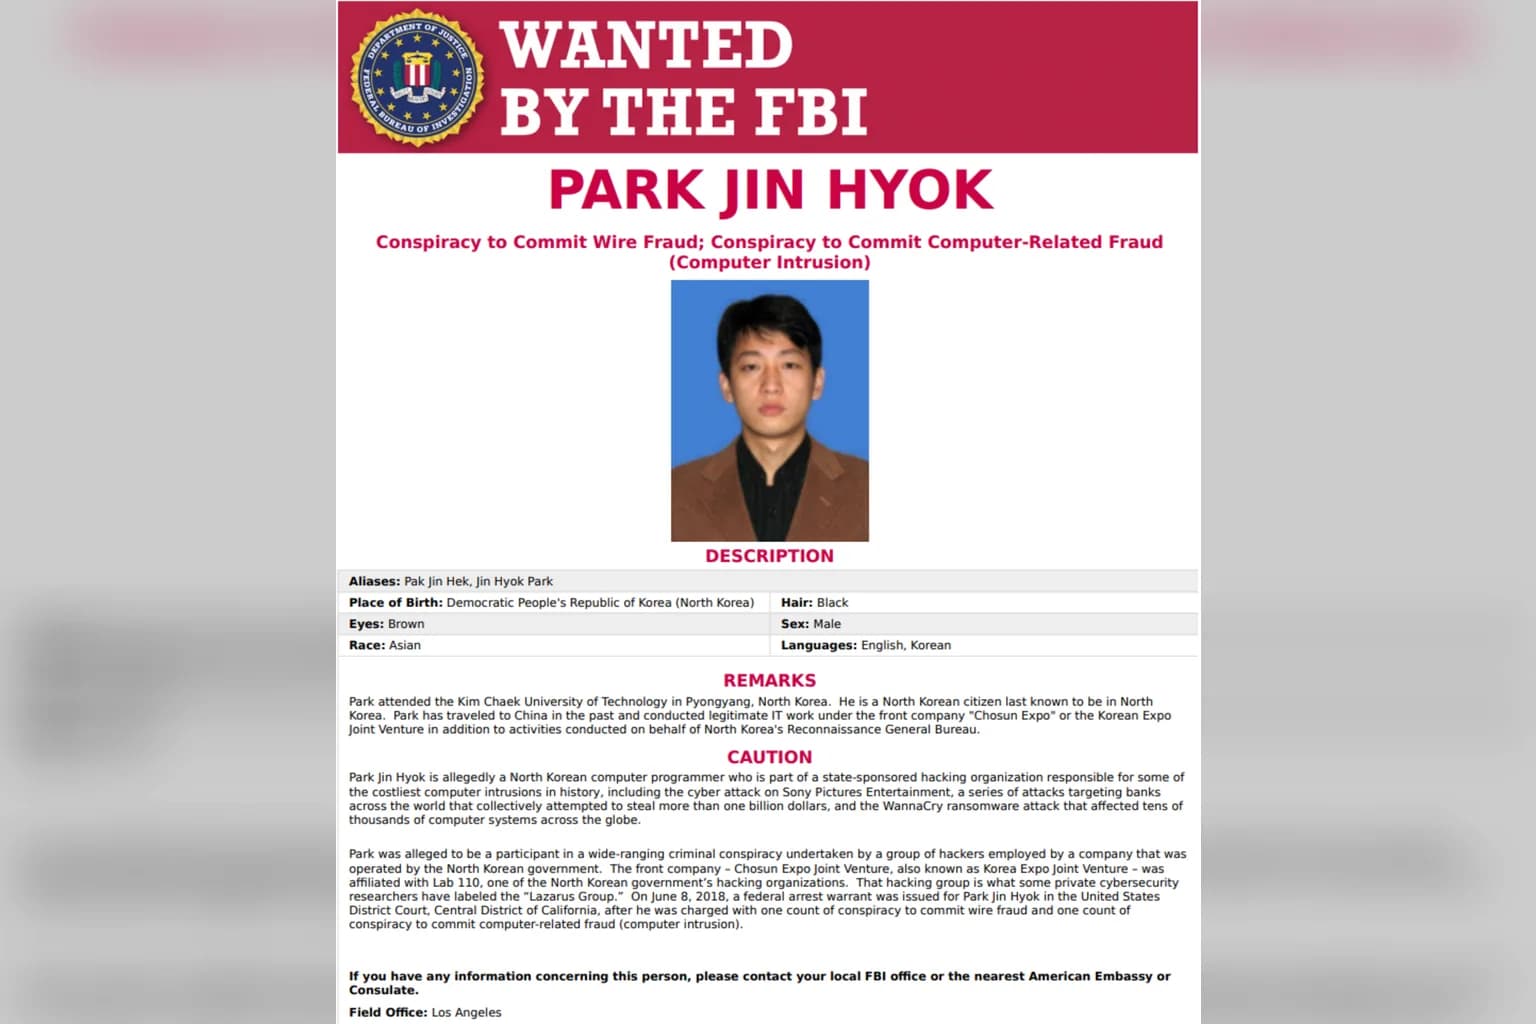
The FBI, the Secret Service and blockchain analysts identified TraderTraitor, a North Korean state-backed group also known as the Lazarus Group, as the organiser of the attack.
The intrusion began in June, when a Binance developer downloaded a tampered installer apparently distributed through a malicious Google advertisement. Binance security teams detected the malware installation and replaced the worker’s device.
In September, another Binance engineer was contacted through a legitimate job-hunting platform by people presenting themselves as recruiters. The fake company representatives used social media accounts with personal images to establish trust through a series of calls and interviews.
During a second fake interview, the engineer was told to download an “assignment”. It was malware.
The software used obfuscation techniques to evade detection and replaced part of a legitimate development tool with a malicious version, giving the attackers backdoor access.
By October 20th, the attackers had used the compromised computer and Binance’s internal artificial intelligence tool to take control of wallets belonging to the developer compromised in June and a third employee.
On October 29th, they logged into the third employee’s computer and began their main assault on Binance’s systems. The attackers then used a special authorisation to make Binance’s hot wallet transfer funds automatically to them. The theft took place on Thursday.
Richard Teng, Binance’s co-chief executive, said the company’s investigation had found other weaknesses beyond the laptop first identified. “Our subsequent investigation has uncovered additional points of breach,” he said.
Binance suspended withdrawals globally while it restored normal operations. It reopened on Sunday after replacing approximately 95% of the stolen assets with corporate treasury, futures insurance and emergency reserve funds, though customers then withdrew $3.6 billion.
The company said it had set aside more than $6.3 billion to cover all losses linked to the attack, and that approximately 95% of the stolen assets had been covered by Saturday. Between 06:00 and 15:30 GMT on November 1, Binance processed $4.649 billion in withdrawals and $1.01 billion in deposits, for a net outflow of approximately $3.64 billion.
Sunday’s net withdrawals represented just over 2% of the $171 billion in assets Binance had under management. The exchange operates the world’s largest cryptocurrency platform and has approximately $157 billion to $171 billion in assets under management.
The FBI, the Secret Service and IRS Criminal Investigation observed the hackers converting the stolen assets primarily into Ethereum. They said they expected further laundering through decentralised finance platforms and instant cryptocurrency exchange services.
Alec Zebrick, a senior manager in global services at Chainalysis, told the BBC’s Today Programme that funds tied to the theft were still being actively laundered. Chainalysis said the attacker had used laundering patterns it had not seen before.
On Saturday, the FBI published cryptocurrency wallet addresses linked to the group and asked industry partners to block transactions involving them.
TraderTraitor had previously been blamed for the then-record $1.5 billion hack of the cryptocurrency exchange Bybit in 2025. Binance said it had prevented 57 suspected North Korea-linked cyber threat cases.
North Korea denied responsibility. Kim Yo Jong, a top Democratic People’s Republic of Korea official and sister of leader Kim Jong Un, said on Tuesday that the allegations were another “sinister attempt” by the US to damage Pyongyang’s public image.
Binance said it would invest more in artificial intelligence tools to detect threats, bring in third-party cyber experts for a full-scale review and seek to establish a security research fund.
Comments (0)