
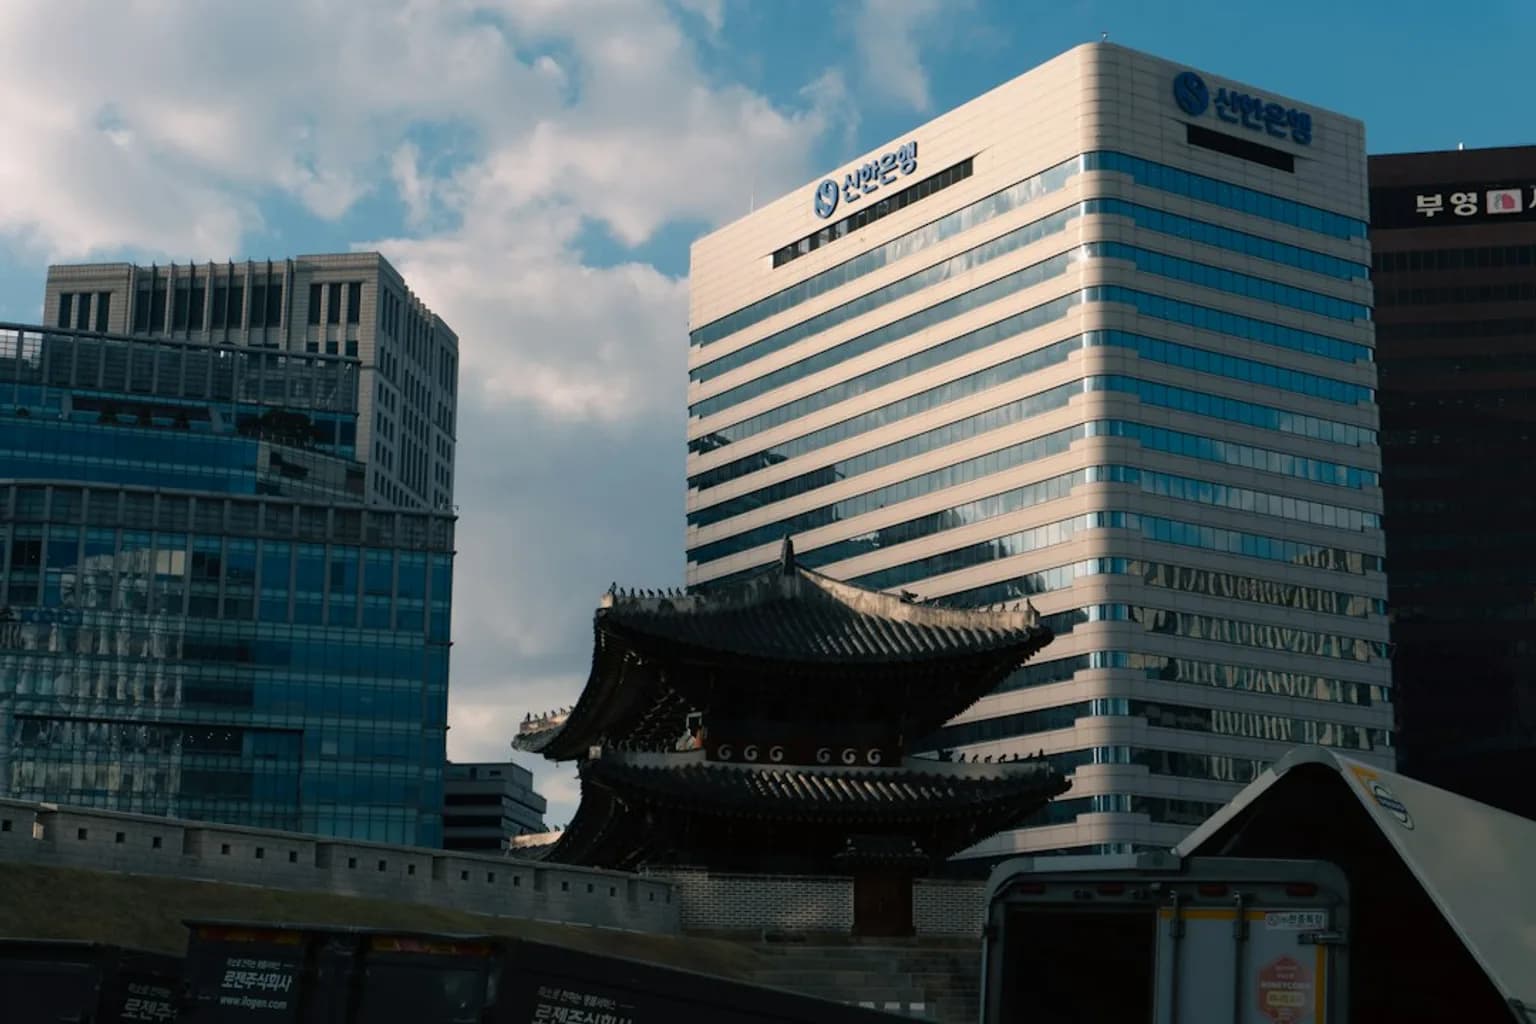
Shinhan Bank said on Thursday, 1 October, that hackers had breached its communications infrastructure, exposing data belonging to approximately 25,000 clients.
Further breaches followed at Hana Bank and BNK Busan Bank on Friday, while an internal review at KB Kookmin Bank found that more than 100 customer records had been leaked after an external intrusion.
The damage extended beyond the banks. About 40,000 customers were affected at Yegaram Savings Bank, while Hyundai Capital said personal information belonging to 146 mortgage loan solicitors had been exposed.
The Financial Services Commission, or FSC, called an emergency meeting after the additional damage at Hyundai Capital and Yegaram Savings Bank was confirmed. The regulator mandated comprehensive security assessments by all banks and credit card companies on Friday, 2 October.
Initial investigations found that some attackers had focused on external websites and servers used by loan agents and employees. These systems had received less security monitoring than core financial infrastructure. The targets included Shinhan Bank’s loan-agent service and KB Kookmin Bank’s mobile work-support system, systems that often use artificial intelligence agents.
Shin Jin-chang, the FSC secretary general, chaired an emergency meeting to share intelligence on the attacks and coordinate the response. He said financial firms needed exhaustive reviews of every IT system that can be reached from outside their networks.
The FSC told companies to list all externally accessible IT assets and services, examine security weaknesses and check their access controls. It also ordered them to limit the external exposure of sensitive data and ensure strong authentication for access to internal information.
Financial Services Commission Chairman Lee Eog-weon called for swift, thorough checks across the sector after an emergency meeting on Sunday with executives from financial institutions and industry groups. Lee said authorities could not rule out the use of artificial intelligence in the attacks and urged faster development of security systems that can use AI against AI-powered threats.
The FSC, the Financial Supervisory Service and the Financial Security Institute have started on-site inspections at four affected banks. The commission said it would gather the findings promptly and use them to develop new plans for digital security across the financial industry.
Authorities still need further verification to establish whether the breaches were the work of the same hacking group. An emergency inspection meeting was scheduled for 4 October at Government Complex Seoul, with heads of financial associations and chief executives of affected companies due to attend.


Comments (0)